Microsoft 365 security posture assessment
Every CIS and CISA control your tenant fails, the setting behind it and how to fix it, ranked by risk. First results arrive minutes after you connect.
What is a Microsoft 365 security posture assessment?
A Microsoft 365 security posture assessment checks how your tenant is configured against a security benchmark, such as the CIS Microsoft 365 Foundations Benchmark or CISA's secure configuration baselines, and lists the controls you fail. It covers identity, email, sharing, Teams and logging settings, and it tells you which gaps to close first.
365TUNE runs the assessment from a read-only connection. Each failed control shows its benchmark ID, the setting, where it lives, the value it should have and a severity. The tenant gets a score from 0 to 100, so you can see the effect of every fix.
365TUNE checks 300+ controls from the current CIS Microsoft 365 Foundations Benchmark, CISA's SCuBA secure configuration baselines and community-driven best practices.
What Secure Score shows, and what it leaves out
Microsoft Secure Score, in the Defender portal, ranks Microsoft's own recommendations by points. It's a useful to-do list, but it isn't organized by CIS or CISA controls. When an auditor or a cyber insurance form asks about a specific CIS control, Secure Score doesn't say whether you pass it.
The free tools that do check the benchmarks take work. CIS-CAT Pro needs a CIS SecureSuite membership, CISA's ScubaGear runs as a PowerShell module, and both produce a report for one tenant on the day you run them. 365TUNE checks the CIS and CISA controls on every scan, daily or on a schedule you set, for one tenant or every tenant you manage, and keeps each result so you can see what changed.
Microsoft documents the setting behind the example control below in Configure how users consent to applications.
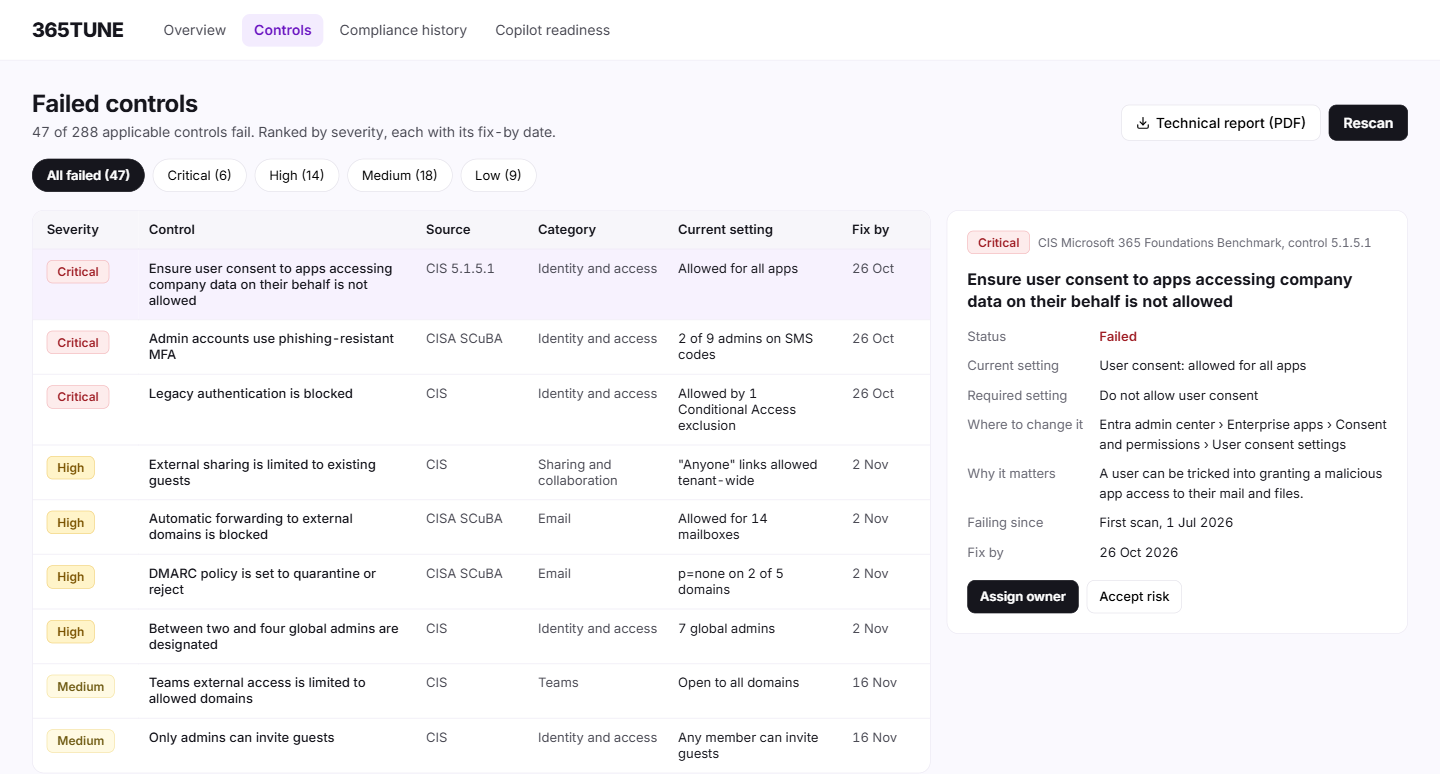
One failed control, the way you'll see it
| Field | Example |
|---|---|
| Control | Ensure user consent to apps accessing company data on their behalf is not allowed |
| Benchmark | CIS Microsoft 365 Foundations Benchmark, control 5.1.5.1 |
| Status | Failed |
| Current setting | User consent: allowed for all apps |
| Required setting | Do not allow user consent |
| Where to change it | Entra admin center › Enterprise apps › Consent and permissions › User consent settings |
| Why it matters | An attacker can trick a user into granting a malicious app access to their mail and files, without a password |
| Severity | High, fix within 14 days |
How it works
- Connect read-only. Grant 365TUNE read access to your tenant. The scan can't change any setting.
- Scan. It reads your identity, email, sharing, Teams and logging settings and checks each against the CIS and CISA controls.
- Score. Each control passes or fails. Failed controls get a severity and a fix-by date, and the tenant gets a score.
- Fix. Work down the list in your admin centers, then rescan to see the score move.
What you get
| Finding | What 365TUNE checks | What you do next |
|---|---|---|
| Identity and access | MFA registration and enforcement, Conditional Access policies, admin roles, legacy authentication, app consent | Close the critical gaps first: admins without MFA, legacy sign-in still allowed |
| Anti-phishing, anti-spam and malware policies, DKIM and DMARC, external forwarding | Fix the policy named in the finding | |
| Sharing and collaboration | SharePoint and OneDrive external sharing, "anyone" links, Teams guest and external access | Tighten the tenant default, then the sites that override it |
| Logging and audit | Unified audit log on, mailbox auditing, log retention | Turn it on today; you can't investigate what wasn't logged |
| Score and history | A score per category and overall, with each scan kept | Show the trend to leadership |
| Reports | A summary for leadership and a technical report with remediation steps, both as PDF | Send each to the people who act on it |
For IT teams and MSPs
For IT teams
Answer the auditor, the CISO and the cyber insurance form from the same report, with a benchmark ID next to every answer.
For MSPs
Score every customer tenant against the same controls, see which customers are most exposed and send each one a report of the gaps you closed, under your own brand.
Security of the connection
The assessment needs read-only access to your tenant. Anything that writes, such as restoring a setting, asks for its own consent, and only for the permissions that task needs. 365TUNE is ISO 27001 certified, has a SOC 2 Type II report and doesn't use your data for training.
See which controls your tenant fails
Connect read-only and get your score and failed controls in minutes.
Questions about Microsoft 365 security assessments
How do I run a Microsoft 365 security assessment?
Pick a benchmark, usually the CIS Microsoft 365 Foundations Benchmark or CISA's baselines, then check each control against your tenant's settings. You can do it by hand with the PDF, with a PowerShell tool such as ScubaGear, or with 365TUNE, which checks every control from a read-only connection and keeps the results.
What's the difference between CIS and CISA controls?
The Center for Internet Security publishes the CIS Microsoft 365 Foundations Benchmark, used widely by auditors and insurers. CISA, the US Cybersecurity and Infrastructure Security Agency, publishes the SCuBA secure configuration baselines, required for US federal agencies. They overlap heavily. 365TUNE checks both.
How often should we assess our tenant?
Admins change settings all the time, and Microsoft keeps adding new ones, so a yearly assessment goes stale fast. 365TUNE re-checks your controls daily, or on a schedule you set, and shows what changed. Compliance monitoring keeps that record for auditors.
Does the assessment fix the gaps for us?
No. The assessment is read-only. Each finding names the setting and its required value, and your admins make the change. Configuration drift can restore approved settings once you grant it write access for that task.
Can MSPs assess every customer tenant?
Yes. Connect each customer tenant over GDAP or with its own consent. Each gets its own score and findings in one dashboard, and its own report under your brand.